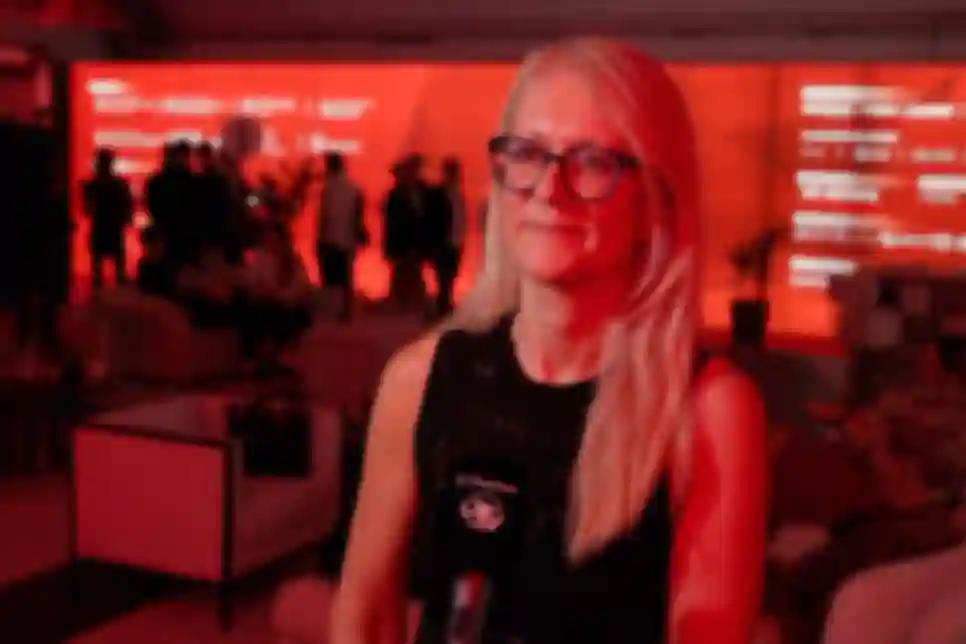
Cybersecurity maturity varies considerably among Croatian businesses. “Some entrepreneurs have a higher level of awareness and implementation of cybersecurity, while others are at a lower level,” Martina Dragičević, Director of Regulatory Affairs, EU Funding and Wholesale at A1 Croatia and a participant in the Croatian Employers’ Association’s ICT cybersecurity coordination, tells ICTbusiness Media – ICTbusiness.info. The gap becomes particularly important as regulatory requirements expand.
Dragičević refers to discussions within the Croatian Employers’ Association concerning national cybersecurity legislation and its implementation. Many companies, she says, are still working to understand exactly what the rules require and how to translate those requirements into internal procedures. “It is important for businesses to understand their obligations,” Martina Dragičević emphasises.
Small and medium-sized enterprises face particular constraints. They may recognise the importance of protection without having the people or resources to establish a comprehensive programme independently. Dragičević also mentions two million euros in support intended to help companies take initial steps towards stronger cybersecurity. “Businesses need support in this process,” Martina Dragičević says.
Artificial intelligence adds another layer of complexity. It can improve productivity and help defenders identify threats, but attackers can also use it to increase the effectiveness of malicious activity. Companies therefore need to consider why they deploy AI, how it is governed and what risks its use creates. “Artificial intelligence is a tool for both sides,” Martina Dragičević points out.
For organisations uncertain where to begin, she recommends a staged approach. Management should first understand its responsibilities and principal risks, then draw on qualified external expertise where necessary. Staff education and clearly defined internal duties are essential if policies are to translate into action. “The management board must know what its responsibilities are,” Martina Dragičević stresses.
Written procedures become especially valuable during an incident. An organisation needs to know who makes decisions, who carries out specific actions and how quickly those actions must happen. Without such preparation, even an otherwise capable team can lose critical time when a breach occurs. “You need to know what to do when an attack happens,” Martina Dragičević explains.
Her conclusion is that cybersecurity cannot be reduced to purchasing protective technology. It requires a combination of knowledge, governance, planning and technical measures, with no promise of absolute safety. For businesses facing new obligations, the priority is to build a workable system of responsibility before a crisis exposes the gaps.